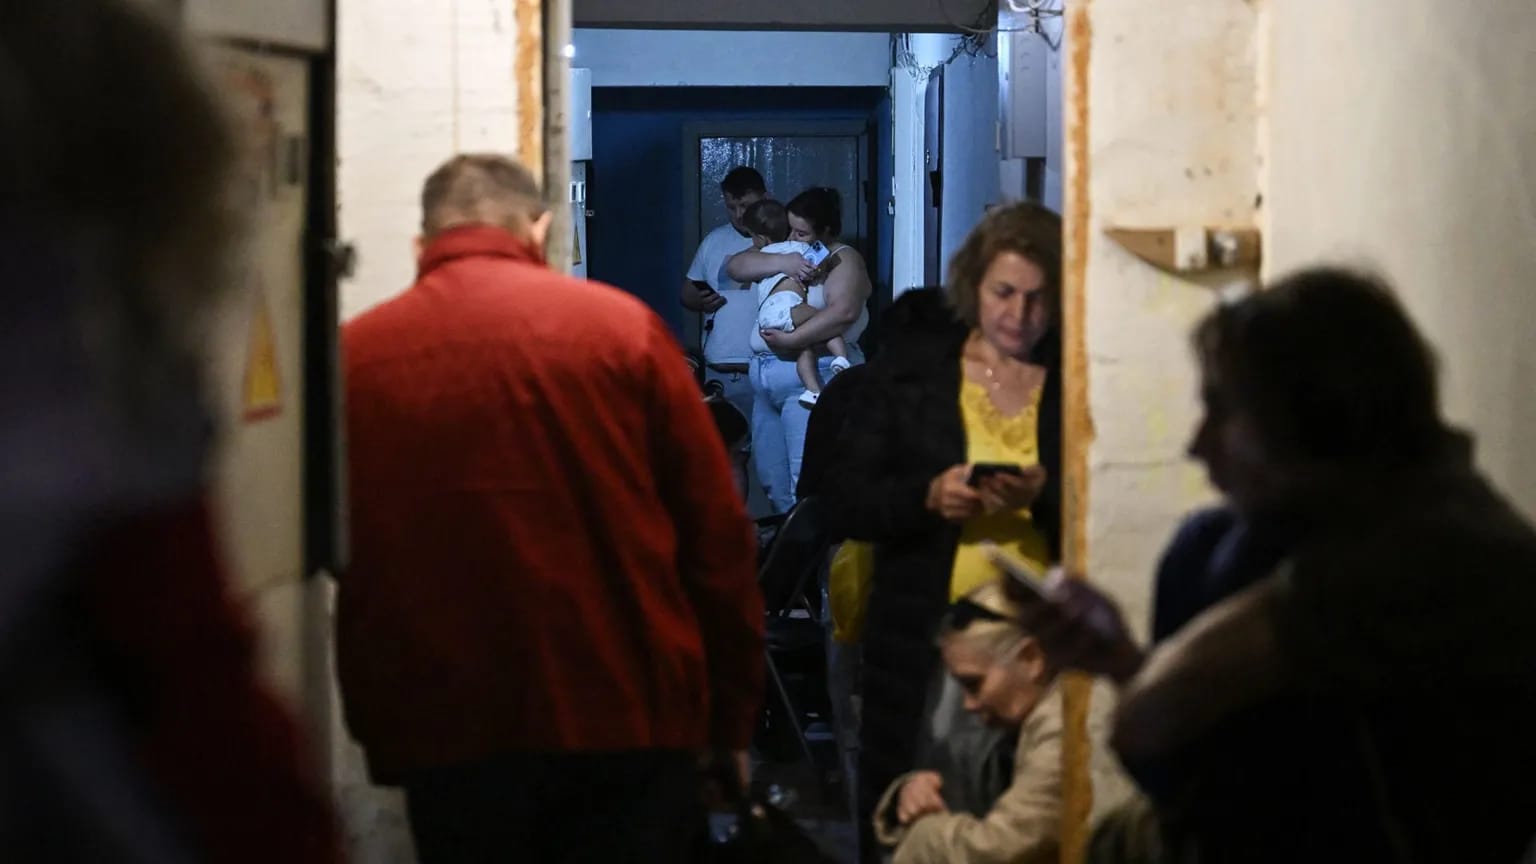
Ukraine’s air raid alert application reportedly suffered a cyberattack on Sunday, sending false warnings about radiation hazards, chemical attacks and possible street fighting in Kyiv and other areas. The incident prompted authorities to urge residents to remain calm and rely on verified information, as the country continues to face security threats amid its war with Russia.
The Ukrainian Air Force said the application appeared to have been affected by hostile interference. Officials stressed that there was no radiation threat and advised the public to follow updates through the military’s official communication channels.
The false notifications appeared at a particularly sensitive time, when Ukrainians have become accustomed to monitoring emergency alerts to protect themselves from Russian missile and drone attacks. The country’s air raid warning system plays an important role in informing people when they should seek shelter.
According to reports, the compromised application displayed warnings suggesting that Kyiv and other locations were facing nuclear and chemical dangers. Some notifications also referred to possible fighting in the streets. Another false message claimed that Russia’s Oreshnik hypersonic missile had been deployed.
The messages caused concern because they appeared through a system that residents depend on for information about immediate threats. However, Ukrainian authorities clarified that the notifications did not reflect the actual security situation.
The Air Force issued a public warning on Telegram, saying the application had probably been subjected to hostile interference. It specifically rejected the radiation warning and urged people not to panic.
Ukraine’s Ministry of Digital Transformation subsequently said the application was not operating normally. However, authorities confirmed that alternative methods of communicating emergency warnings remained available, including air raid sirens.
The incident raised concerns about the vulnerability of digital emergency systems during wartime. Such applications are designed to deliver urgent information quickly, allowing residents to respond to incoming attacks. If false information enters these systems, it can create unnecessary fear, undermine public confidence and make it more difficult for people to distinguish genuine threats from fabricated warnings.
Ukraine’s Centre for Countering Disinformation also warned that the threat information displayed through the application did not match the actual situation. Officials encouraged residents to verify reports through official sources rather than relying exclusively on notifications received through the affected service.
Natalia Zabolotna, governor of Ukraine’s Vinnytsia region, warned residents about the reported cyberattack and advised them not to click on links included in suspicious messages. The warning raised the possibility that the incident could involve attempts to direct users towards harmful links or obtain sensitive information, although the precise method of the attack had not been publicly established.
Ukraine’s Centre for Strategic Communications blamed Russia for the incident. However, publicly available information did not independently establish who was responsible for the alleged intrusion. No group had publicly claimed responsibility at the time of the initial reports.
The incident also came amid continuing cyber tensions between Moscow and Kyiv, whose conflict has extended beyond the battlefield to include digital infrastructure, communications and information systems. Emergency applications have become particularly important in Ukraine because residents often have limited time to react when authorities identify an incoming missile or drone threat.
In a separate development, Russia’s Emergencies Ministry reported that its own mobile application had suffered a major cyberattack. According to the ministry, the incident allowed false information to be distributed to members of the public.
The Russian ministry announced the incident early Monday and said the attack had affected its emergency communication service. The application is used to provide information about potential dangers, including drone attacks and other emergencies.
Russian authorities said they were working to address the problem and restore the affected service. However, the available reports did not establish whether the incident involving Russia’s application was connected to the disruption reported by Ukraine.
The simultaneous reports from both countries highlighted the growing importance of cybersecurity in emergency communication. Although the two incidents occurred within a short period, officials had not provided evidence confirming that they were part of a coordinated operation.
The incidents also coincided with the end of a temporary local ceasefire in Ukraine’s southern Kherson region. The truce, which had lasted six days, was intended to provide a period of reduced fighting in the affected area. Its conclusion added to concerns about the security situation as both countries continued their military operations.
The false notifications demonstrated how digital interference can complicate an already difficult situation for civilians living under the threat of attack. Emergency alert systems depend on public trust, and people must be able to rely on the information they receive when deciding whether to leave their homes or seek shelter.
Cybersecurity experts have repeatedly warned that attacks targeting public information systems can have consequences beyond the immediate disruption of technology. False warnings may spread confusion, encourage people to take unnecessary risks or cause them to become less responsive to genuine alerts in the future.
For Ukraine, maintaining reliable emergency communications remains essential as the country continues to defend itself against Russian attacks. The authorities’ response to Sunday’s incident focused on reassuring residents that there was no radiation threat and directing them towards trusted information channels.
The episode also underlined the importance of maintaining backup warning systems so that emergency information can continue reaching the public even when a digital service becomes unavailable.
While Ukrainian officials attributed the incident to hostile interference and blamed Russia, the precise circumstances of the reported cyberattack remained unclear. The separate report of a cyberattack against Russia’s emergency application added another dimension to the situation, but whether the two incidents were linked had not been established.
Authorities in both countries now face the challenge of restoring confidence in their emergency communication systems and ensuring that residents can distinguish authentic warnings from misleading messages during an ongoing conflict.
Comments
No comments yet. Be the first.
Related Stories
Related Stories
First published 2 November 2026. Spotted an error? Read our corrections policy.